I wanted a flip phone that could run exactly one sideloaded app. The TCL 4058G refuses to install any, so this turned into rooting a TCL 4058G (Gflip6_NA_OM, MediaTek MT6739, Android 11) from an Apple Silicon Mac — and writing down what it cost.
Two reasons this repo exists:
- Everything in this community assumes Windows or Linux. flip2’s
autobooter.pyreads COM ports out of the Windows registry, and mtkclient is broken at import on any Mac without macFUSE. Both are fixed here. - Most of the time was lost to failures that produce no error message. A property that reads empty whether or not it’s set; an init
.rccommand silently deleted at parse time;ddhalf-succeeding and exiting 0. Those are written up in detail, because they’re what actually costs you the day.
Is this for you?
Directly: TCL 4058-family flip phones (4058G, 4058W, T408DL, 4058E and relatives) on macOS. Partly, and worth reading anyway:
- Anyone whose
ro.vendor.*property “won’t set” —getpropis very likely lying to you. The property resolves to an SELinux contextadb shellcan’t open, and both lookup paths fail silently in the same direction. That one cost about eight flash-and-reboot cycles chasing a bug that didn’t exist. - Anyone Magisk-patching a 32-bit-only Android device. Patching on an arm64 emulator produces an image that bootloops the phone, with no explanation.
- Anyone injecting boot scripts through Magisk’s
overlay.d, where some.rcrules fail silently. - Anyone working with a MediaTek device on macOS.
The short version of the route
Fastboot is only reachable through a 2–3 second preloader window (adb reboot bootloader does not work). BROM never enumerates and mtkclient can’t talk to this preloader at all, so there’s no way to read flash before unlocking — the backup can’t come first, however much you want it to.
bootseq.py FASTBOOT  ->  fastboot flashing unlock   (WIPES, confirm on handset)
   -> flash recovery2.img   (destroys stock recovery; unavoidable)
   -> dump-from-recovery.sh -> your own stock boot.img
   -> patch-boot.sh         (on the phone, never an emulator)
   -> flash-boot-from-recovery.sh
   -> inject-endurance.sh   (vendor install-block, baked into the ramdisk)
   -> install the Magisk app -> grant shell root
The tools
| Script | What it does |
|---|---|
bootseq.py | macOS port of flip2’s autobooter — the only way into fastboot |
usbwatch.sh | tells “never enumerated” apart from “enumerated, handshake failed” |
recon.sh | read-only device survey |
dump-from-recovery.sh | 41 partitions out of a recovery with su |
setup-magisk.sh | extracts the armeabi-v7a Magisk kit and asserts every binary is 32-bit ARM |
patch-boot.sh | runs Magisk’s patcher on the phone, then verifies the injected /init is 32-bit |
flash-boot-from-recovery.sh | writes a boot image and reads it back to prove it landed |
inject-endurance.sh | bakes the vendor install-unblock property into the ramdisk |
install-fota-guard.sh | re-disables the OTA updater on every boot |
The scripts carry their reasoning in comments — usually naming the specific failure that forced the code. They’re meant to be read, not just run.
⚠️ Don’t publish your partition dumps
There’s no stock-firmware ROM in the repo, and you shouldn’t make one from your handset either. proinfo carries your IMEI. nvram/nvdata/persist and friends carry per-unit radio calibration — flashing yours onto another phone can leave its radio transmitting wrong. And strings finding no IMEI isn’t clearance; it’s BCD-encoded. Keep your dumps, restore from your dumps, don’t upload them.
What it’s for
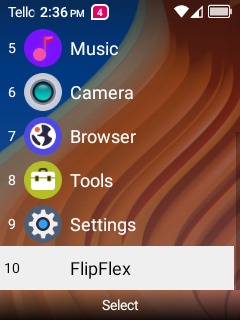
This is the groundwork for FlipFlex (Plex) and FlipFin (Jellyfin) — full media clients for the flip phone, with offline downloads. That’s FlipFlex sitting in the phone’s own Menu, at item 10.
Warning: unlocking wipes the device and the write steps can bootloop it. Everything here was run against exactly one handset (build UPCI/RP1A.200720.011). The 4058 family is a zoo of models and firmware branches — check yours against the repo before writing anything, and keep your own boot.img somewhere safe. No warranty; you can brick your phone.
The route itself is neutronscott/flip2’s — recovery2.img, the autobooter concept and the .rc recipe that finally worked all come from there. This is the macOS port, plus the failure modes that cost the most to rediscover.
Free and open source, and it’s staying that way. If it saved you some time, you can buy me a coffee.